Enforce Jailbreak Policy
Detect jailbroken iOS devices and enforce organizational security policies through the MDM blockJailbrokenDevices restriction key.
Configuration
Jailbreak detection is controlled by the blockJailbrokenDevices MDM restriction key.
- Type: Boolean, number, or string (parsed as boolean)
- Default when absent:
false - Platform: iOS only
This restriction has no effect on macOS or visionOS, as jailbreaking is specific to iOS devices.
Block Behavior
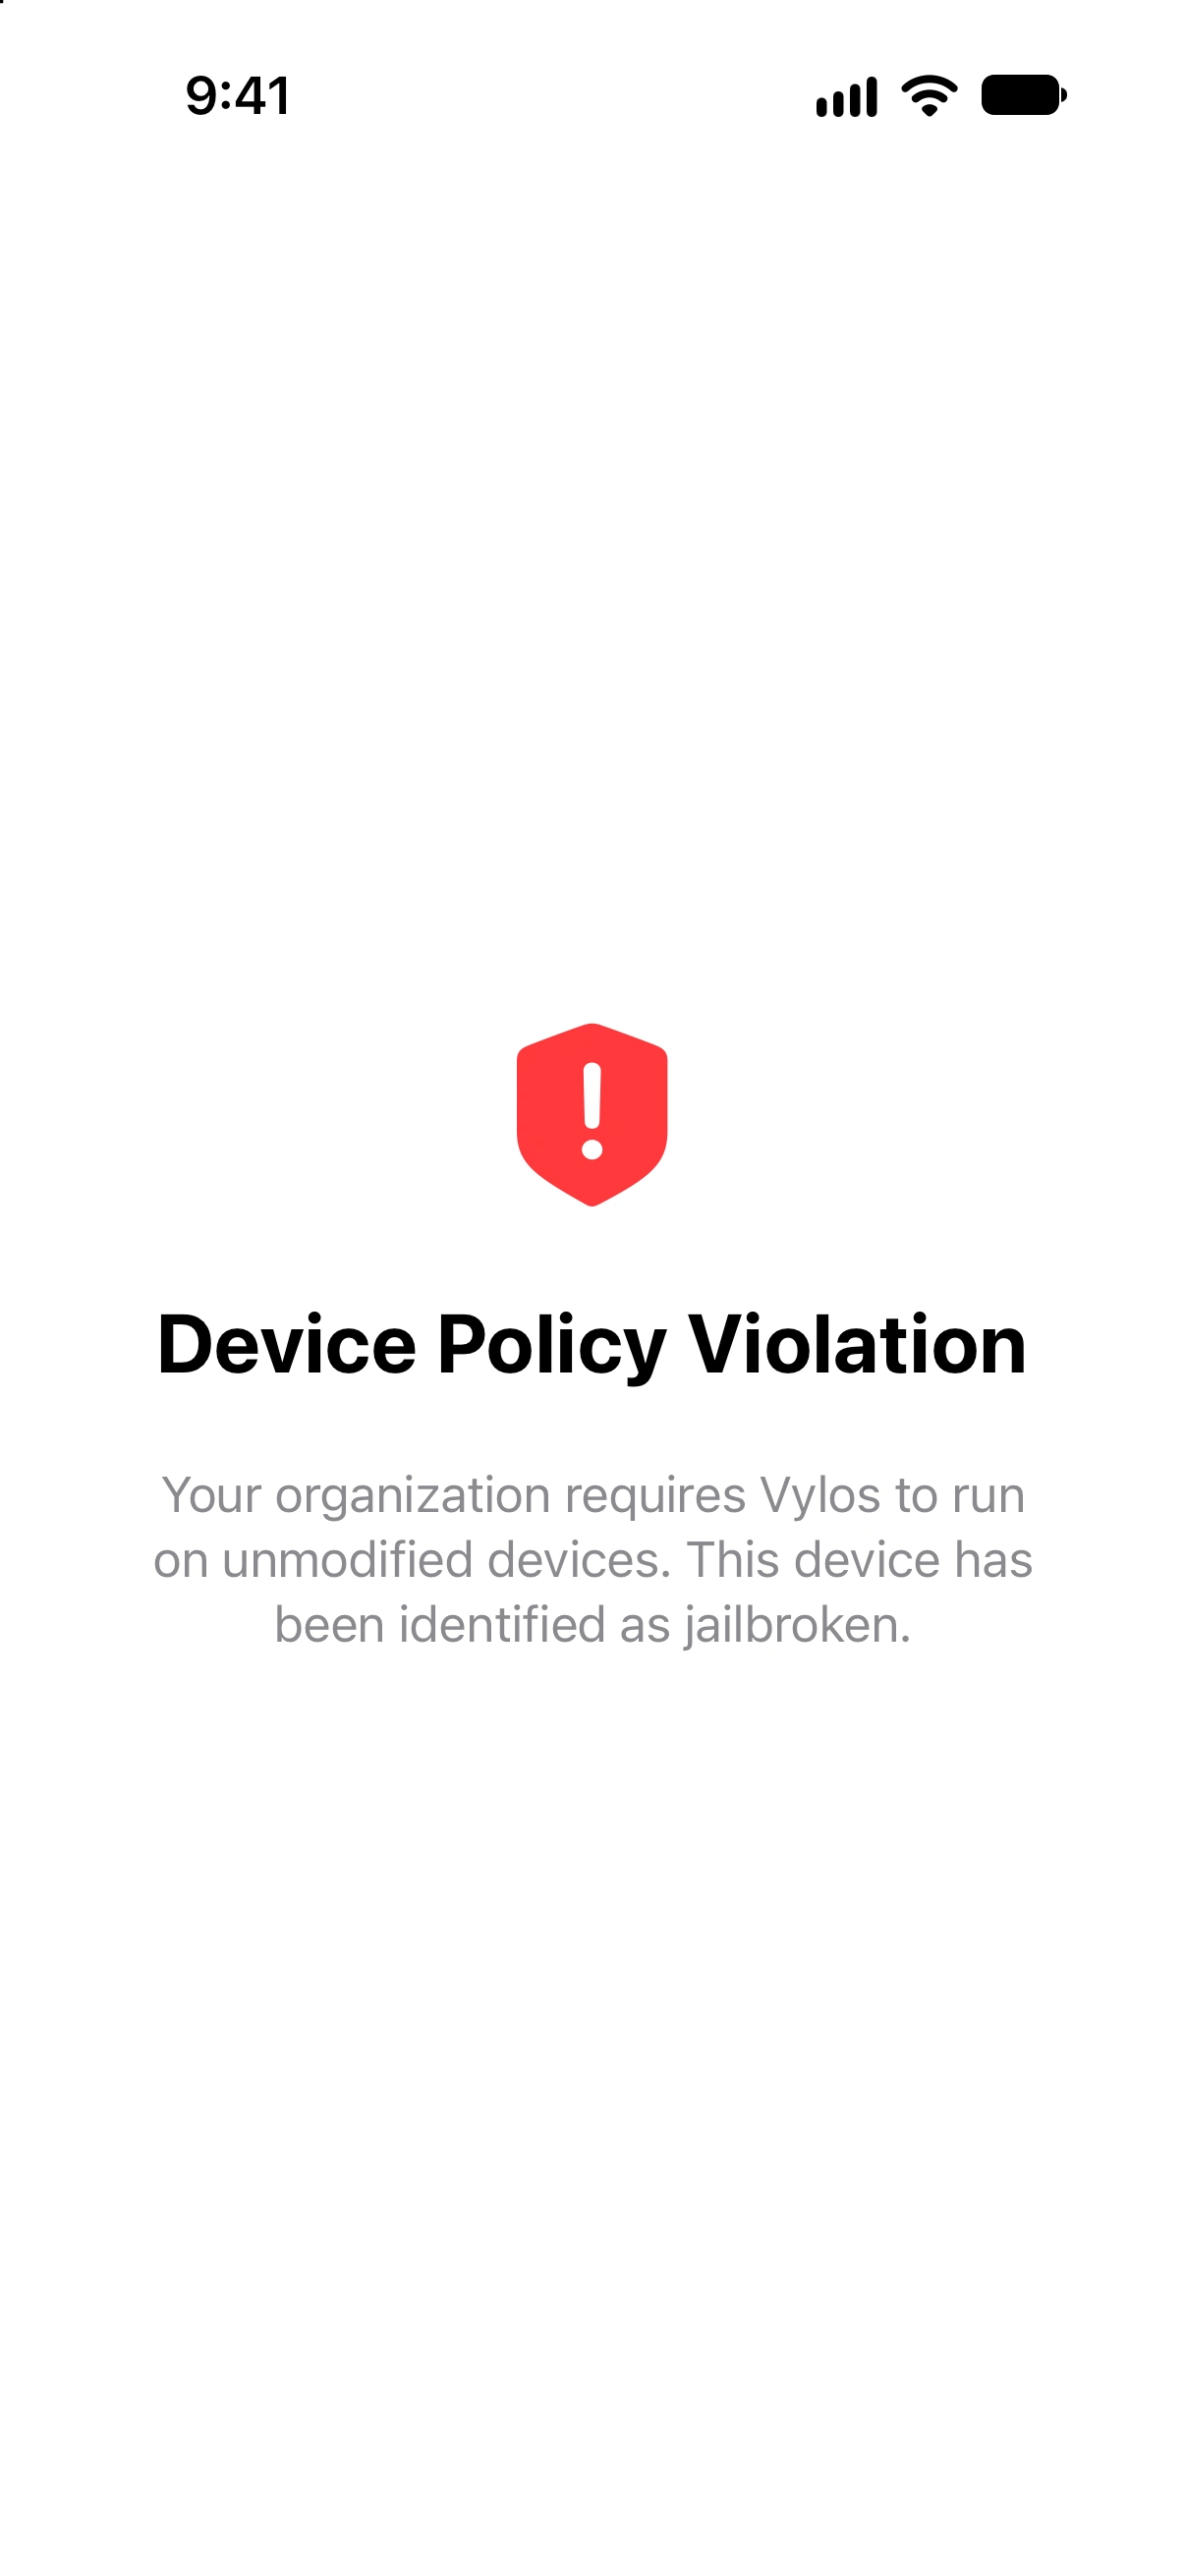
When blockJailbrokenDevices is set to true and a jailbreak is detected, Vylos fails closed. The app displays a full-screen block view titled "Device Policy Violation."
The policy message explains that the organization requires Vylos to run on an unmodified device. The user can't dismiss the block screen.
At the same time, Vylos:
- Disconnects every active Vylos tunnel, including managed tunnels.
- Disarms every Vylos On-Demand tunnel so iOS doesn't keep requesting a connection.
- Makes the packet-tunnel extension reject manual, system, and On-Demand start requests while the block remains active.
- Removes app-created tunnels from Shortcuts discovery and refuses previously saved tunnel actions.
Detection runs on the initial app launch, when managed jailbreak policy changes while Vylos is open, and whenever Vylos returns to the foreground. Existing connections are stopped as soon as Vylos evaluates a positive detection.
Detection Approach
Vylos uses complementary integrity checks for jailbreak-related artifacts, registered tooling, sandbox compromise, and runtime injection. If any layer returns a positive result, Vylos treats the device as jailbroken for the managed policy.
The public documentation intentionally describes these categories without publishing the exact indicators. This keeps the administrator contract clear without turning the security guide into a bypass checklist.
Data Safety
No tunnel configuration data is lost when the jailbreak block is active. Vylos changes only runtime connection state and the saved On-Demand armed state: tunnel configurations, Keychain entries, and app settings remain intact and become accessible again when the block condition is resolved.